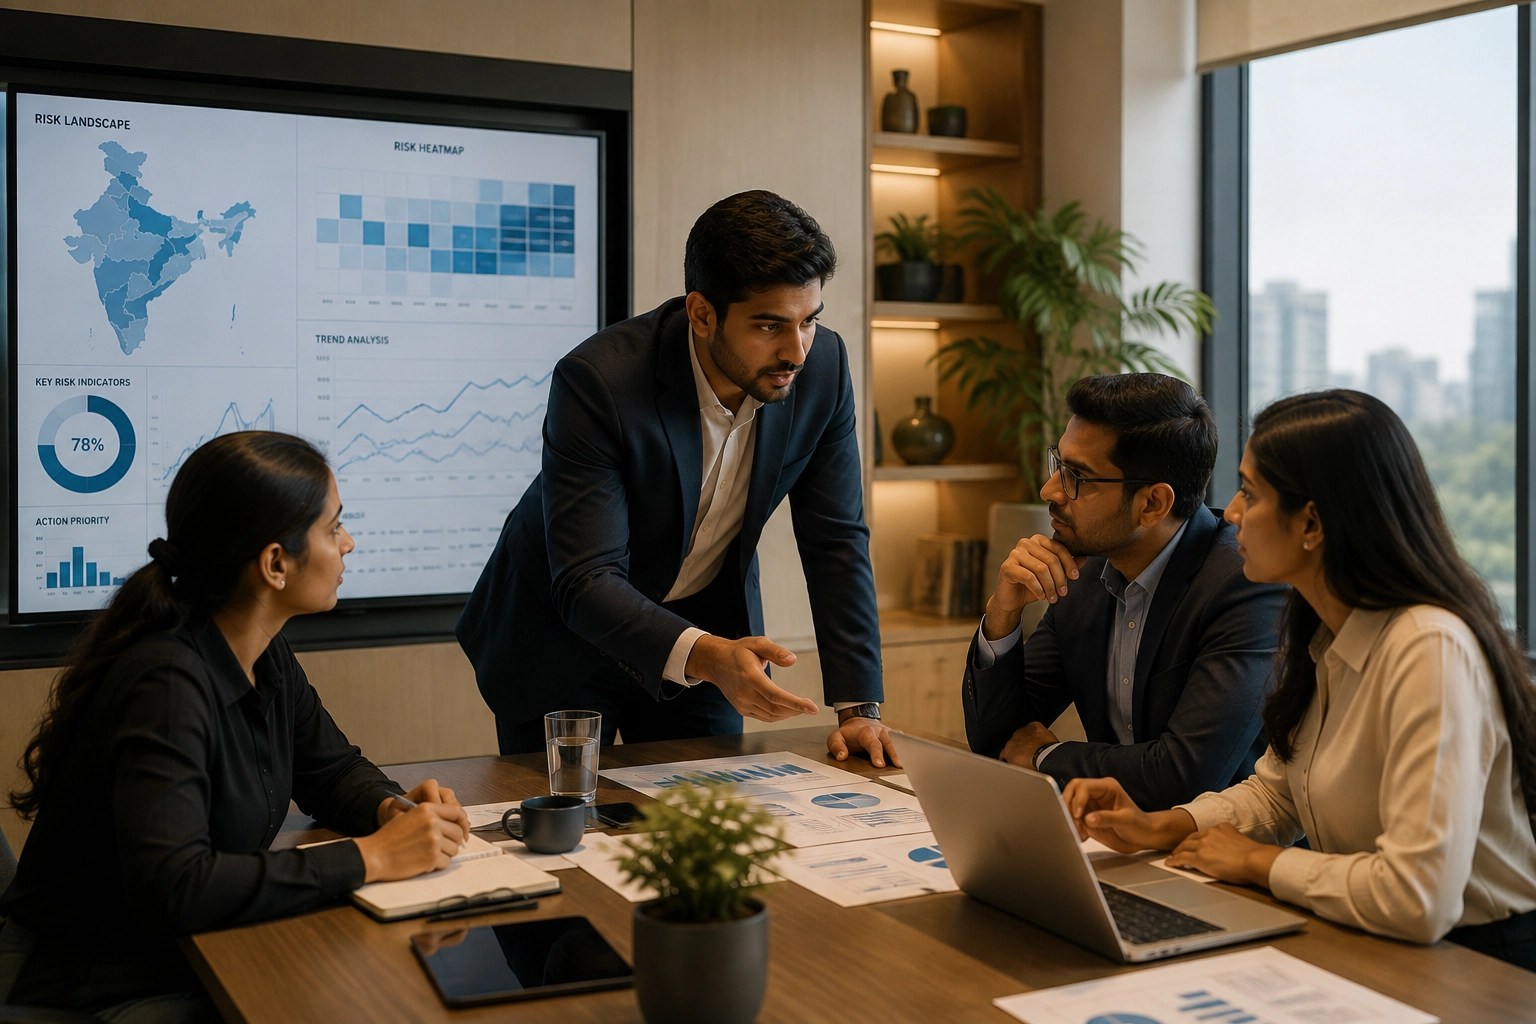
IIRIS designs and operates risk-management frameworks that connect business objectives, operational indicators and decision rights. We structure enterprise risk registers, issue workflows, control libraries and management dashboards so that risks can be captured consistently, escalated efficiently and reported with board-ready clarity.
 Explore Service
Decision Intelligence for Risk-Ready Operations.
IIRIS delivers advisory as an intelligence-enabled operating service rather than a one-time report. We combine structured assessments, data review, risk taxonomies and implementation support to help leadership teams and delivery centres convert complex risk signals into prioritised, measurable action. The model is designed for organisations that need advisory depth alongside the repeatability, responsiveness and reporting discipline associated with modern KPO and BPO environments.
Our Services
At IIRIS, we go beyond traditional consulting. As your risk advisory partner, we enable confident decision-making by integrating strategy, governance, and execution support at every stage. Our advisory services are designed to strengthen your organisational resilience, ensure regulatory readiness, and embed security by design.
We design crisis playbooks, escalation matrices, contact protocols and communications workflows that allow distributed teams to act with control under pressure. Table-top simulations, role-based drills and after-action reviews test decision paths before an incident occurs, while clear service-level expectations improve hand-offs across corporate, KPO and BPO operations.
IIRIS translates governance requirements into practical operating workflows. We map obligations to policies, controls, evidence requirements, owners and review cycles; maintain issue and action logs; and create reporting that gives management a reliable view of control performance. This helps regulated and high-growth organisations move from periodic compliance exercises to a disciplined, measurable GRC operating model.
IIRIS helps clients define security architectures that link people, process, technology and governance. Our work covers threat-led design, operating procedures, control standards, command and monitoring workflows, technology requirements and vendor-neutral architecture reviews. The result is a scalable security model that is designed around business operations, not isolated products.
A capability that grows with the organisation
Building depth across risk, governance and security takes years, and keeping it current asks more still. IIRIS provides that depth as a working capability, staffed by specialists and supported by proprietary technology, shaped to what the organisation needs now and ready to widen as that changes.